Procurement Market Intelligence Report
Security Software
Sourcing Guide & Market Intelligence
Smarter cost management starts with comprehensive market intelligence
 United States
 Europe
 Global
Quick Navigation
Security Software Global Overview
Definition
Summary
Security software publishers develop and distribute various programs that protect a system from malware and spyware, including viruses, worms, trojan horses, adware, system monitors, and tracking cookies. Once detected, internal threats are removed and incidents are recorded. Key buyers include financial institutions, government agencies, and technology firms.
This Report Includes:
- Data Encryption
- Data Scanning
- System Vulnerability Fixes
- Fortifying Existing Security Measures
Not in this Report:
- Network Security
- Software Testing
- Cybersecurity Consulting
Global Security Software Procurement Trends
Discover the top international trends affecting procurement in the global Security Software market.
Warning Trends
The European Union’s Artificial Intelligence (AI) Act enters into force
- In August 2024, the European Union (EU) began enforcing its new regulation on artificial intelligence. Although EU legislation, the act will have a major effect on global technological companies operating in the AI space, similar to the General Data Protection regulation.
- The legislation aims to apply a risk-based framework to AI regulation, meaning different AI applications will be treated differently. The law applies a general ban for “unacceptable” uses, such as social scoring and predictive policing.
- For general-purpose AI models, companies will be required to comply with EU copyright law and intellectual property provisions, carry out regular testing, issue transparency disclosures, and implement adequate cybersecurity protections. For “high-risk” AI applications, such as autonomous vehicles, medical devices, financial services, and biometric identification systems, companies must meet stricter requirements in terms of risk-mitigation systems, documentation, human oversight, and cybersecurity.
- Companies that breach the AI Act may face fines ranging from 7.5 million euros or 1.5% of global annual revenues to 35.0 million euros or 7.0% of global annual revenues, whichever amount is higher.
- While the blanket ban on unacceptable systems entered into force in February 2025, most of the obligations do not take effect for a full year. In August 2025, requirements for general-purpose AI will come into effect, and in August 2026, obligations for high-risk AI systems will be enforced.
Neutral
GSA memo asks agencies to review consulting contracts
- The General Services Administration (GSA) recently issued a memorandum asking government agencies to review their consulting contracts with the ten highest-paid firms. The ten firms are Accenture PLC (Accenture Federal Services), Booz Allen Hamilton Inc., CGI Group Inc. (CGI Federal), Deloitte Touche Tohmatsu (Deloitte Consulting), General Dynamics Corporation (General Dynamics IT), Guidehouse Inc., Huntington Ingalls Industries Inc. (HII Mission Technologies), International Business Machines Corporation (IBM), Leidos Holdings, Inc., and Science Applications International Corporation, Inc. (SAIC).
- The memo states that agencies are strongly encouraged to cut non-essential consulting contracts, providing a list of those intended to be terminated by March 7, 2025. By April 19, 2025, agencies must submit their reviews of non-GSA consulting service contracts.
- According to the GSA, the ten consulting firms identified are set to receive $65.0 billion in fees in 2025. The Department of Defense (DoD) has stated its intention to terminate or descope contracts non-essential to the DoD’s purposes; some of the largest market players with high-value DoD contracts include Booz Allen Hamilton, Deloitte, and Accenture.
- According to the Government Accountability Office, in the fiscal year 2023, government agencies spent $478.0 billion on services, with the DoD accounting for $230.0 billion and non-defense agencies accounting for the rest. The DoD spent $21.3 billion on support, professional, and engineering and technical services, while non-defense agencies spent $21.4 billion on professional services, which includes consulting, training, and support services.
- The Department of Veterans Affairs (VA) initially cancelled 875 contracts (amounting to around $2.0 billion) but has currently paused efforts. However, contract terminations across most agencies are expected to continue.
Positive Trends
The DOJ proposes Google breakup in latest tech antitrust action
- In August, Google was found guilty of operating as a monopoly and engaging in anti-competitive practices through the operation of its search engine business.
- In response to this ruling the Department of Justice (DOJ) has stated it will seek a breakup of Google’s business segments, among other similarly harsh penalties. While the actual penalty Google receives must be approved by the judge, the DOJ’s proposed penalties signal a zero-tolerance policy toward tech monopolies.
- During the last few years, the Federal government has significantly increased its enforcement actions against major technology companies in an effort to contest the high level of market share concentration in this sector.
- These actions include high-profile anti-trust lawsuits against Amazon, Apple, and Meta, in addition to the case against Google. Consequently, the results of these lawsuits could significantly affect the structure of a wide range of tech markets.
Global Security Software Market - Suppliers by Region
| Country/Region | Number of Suppliers |
|---|---|
| #1 Europe | 2,150 |
| #2 India | 1,445 |
| #3 South America | 1,400 |
Explore supplier concentration across the globe
We've uncovered the 11 top regions for global procurement, based on feedback from our most strategic clients. Access vendor counts for each unique region when you subscribe.
2
Geography Drilldown - US & Europe
Average Cost of Security Software
United States
2026 Market Pricing$0.00 to $XXX.XX
per year
Average Price
Prices in the Security Software market range from $0.00 to $XXX.XX, depending on Number of Licenses, Security of Layers and Functionality, Level of Technical Support and Reputation. For example, lower prices are associated with 51-100 licenses ($25.00 to $150 per year) and 100+ licenses ($25.00 to $125 per year), whereas higher prices are associated with 1-10 licenses ($0.00 to $200 per year) and 11-50 licenses ($50.00 to $175 per year).
Need the scoop on international price trends?
Between our Europe and Canada collections, we provide price data for 350 markets so you can instantly compare prices across borders. Or, use our custom research services for intel on prices in any region across the globe.
Security Software Category Price Trends
Pricing trends are indicated by the compound annual growth rate (CAGR) during a set period of time. For the Security Software market, prices in the US have grown 0.6% from 2022 to 2025. Meanwhile, the recent three-year CAGR for Europe is +1.7%.
United States (2022-2025)

Europe (2022-2025)
Compound Annual Growth Rate
Wondering where prices are heading?
Price trend forecasts are available to subscribers, along with price driver projections and forward-looking cost structure data.
Cost Analysis - Total Cost of Ownership for Security Software
Total cost of ownership is Medium in the Security Software market. The average cost of ownership differs depending on the contract but generally includes costs negotiated before the contract begins, costs billed during the contract period and unforeseen costs. For example, unforeseen costs in the form of Emergencies may raise the total cost of ownership unexpectedly.
Negotiated Before
Implementation
Billed During
Security
Training
Unforeseen
Emergencies
Buyer Power in Procurement Negotiations
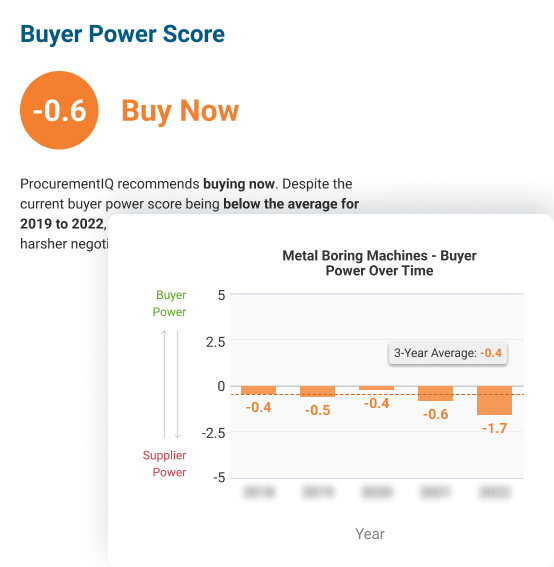
In 2026, buyer power amounts to 0.3 in the United States. Buyer power is most positively impacted by Availability of Substitutes. It is most negatively impacted by Recent Price Volatility. Subscribers can access details on eight other factors that impact buyer power. Learn more
United States
Buyer power forecasts: your glimpse into the future
Develop strategies for the upcoming year and identify unforeseen opportunities for buying now
- Actionable "Buy Now" and "Buy Later" insights
- Near-real-time updates to current and forecast Buyer Power Scores
- Methodology and weightings for Buyer Power Score Components
Supply Chain Risk
The average level of supply chain risk is assessed as Low, which has a positive impact on buyer power. The level of supply chain risk is affected by industry volatility, barriers to entry, competition, import penetration, regulation and industry financial risk. Buyers in this market can mitigate procurement and supply chain management risks by monitoring risk levels for individual first and second tier suppliers:
1st
Tier Suppliers
- Software Publishers
- Computer & Packaged Software Wholesalers
- IT Consultants
2nd
Tier Suppliers
- Intellectual Property Leasing Firms
- Semiconductor Manufacturers
- Computer Manufacturers
Biggest Security Software Suppliers in the US by Revenue
The largest Security Software vendors by revenue in the US are Kaspersky, Check Point Software Technologies Ltd. and Microsoft Corporation. Subscribers can sort and filter by market share concentration, profit level and other factors. Learn more
| Supplier | Operational Size | Headquarters | Number of Employees | Market Share (%) | Market Share Performance (3yr trend) | Total Revenue ($ million) | Profit Level (%) | Risk Level |
|---|---|---|---|---|---|---|---|---|
| International Business Machines Corporation | Global | ARMONK | >10,000 | 5-10 | ||||
| Intel Corporation | Global | SANTA CLARA | >10,000 | 5-10 | ||||
| Broadcom Inc. | Global | PALO ALTO, CA | >10,000 | 5-10 | ||||
| Check Point Software Technologies Ltd. | Global | TEL AVIV, ISRAEL | 1,001-10,000 | 5-10 | ||||
| Darktrace Limited | Global | Cambridge, UK | 1,001-10,000 | 5-10 | ||||
| Kaspersky | US | 5-10 | ||||||
| Microsoft Corporation | Global | REDMOND, US | >10,000 | < 5 | ||||
| Oracle Corporation | Global | AUSTIN, CA | >10,000 | < 5 | ||||
| Hewlett Packard Enterprise Co | Global | SPRING | >10,000 | < 5 | ||||
Looking for a list of suppliers by country?
Subscribers can access vendor information on Canadian and European suppliers, too. We also offer custom research services to help with vendor sourcing anywhere in the world.
Profit Analysis
The average profit margin across vendors in the Security Software market is 29.1% and steady. Profit levels shift depending on suppliers' spend on wages, purchases and overhead. The highest cost component for vendors is Wages. The cost trend for this component is rising, when considering movement between 2025 and 2026. To understand cost forecasts for 2027 and uncover the implications on profit, start your subscription. Learn more
Vendor & Supply Chain Analysis
The current level of profit benefits buyers because it ensures that the average vendor is financially secure and supplier bankruptcies will not disrupt the supply of software or services. High profit margins give buyers more room to negotiate for better deals because vendors have the ability to lower prices.
The medium level of market share concentration somewhat hinders buyers because they may have a hard time sourcing from qualified vendors apart from the few large security software suppliers.
Because suppliers do not rely on many physical inputs to produce security software, supply chain risk is low.
The United States is a net importer of computers, meaning it imports more computers than it exports. While lower manufacturing costs abroad drive down prices for imported computers, relying on imports can lead to potential shortages or price increases if there are supply chain disruptions due to geopolitical tensions, trade disputes, or global crises.
Supplier Information
Broadcom Inc.
Broadcom Inc. is a public company operating globally in the manufacturing, information and professional, scientific and technical services sectors. The company's offerings include central processing units, transistors, database management systems, network security equipment, wireless access points. Founded... Subscribe to learn more
Check Point Software Technologies Ltd.
Check Point Software Technologies Ltd. is a public company operating globally in the manufacturing and information sectors. The company's offerings include network firewall security equipment, network security equipment and security software. Founded in 1993, the company is currently headquartered in Tel Subscribe to learn more
Darktrace Limited
Darktrace Limited is a private company operating globally in the information sector. The company's offerings include security software. Founded in 2013, the company is currently headquartered in Cambridge, England, United Kingdom with an estimated 5500 employees. Subscribe to learn more
Intel Corporation
Intel Corporation is a global integrated device manufacturer that designs, develops, manufactures, markets, and services central processing units (CPUs) and related solutions. It offers CPUs and chipsets, a system on a chip (SoC), or a multichip package based on Intel® architecture that processes data and... Subscribe to learn more
International Business Machines Corporation
International Business Machines Corporation (IBM) is a global integrated computer technology, hardware, software, and services provider. It organizes its business into four segments: Software segment, which provides software solutions for a hybrid cloud platform, data and artificial intelligence, automation,... Subscribe to learn more
Kaspersky
Kaspersky is a private company operating in the information sector. The company's offerings include security software. Founded in 2020, the company is currently headquartered in United States of America. Subscribe to learn more
Avast Software s.r.o.
Avast Software s.r.o. is a private company operating internationally in the information sector. The company's offerings include security software. Founded in 1988, the company is currently headquartered in Prague, Czechia with an estimated 5500 employees. Subscribe to learn more
Bitdefender
Bitdefender SRL is a private company operating globally in the information sector. The company's offerings include security software. Founded in 2001, the company is currently headquartered in Bucharest, Romania with an estimated 5500 employees. Subscribe to learn more
Hewlett Packard Enterprise Co
Hewlett Packard Enterprise Co. is a global technology company developing intelligent solutions for business and public sector enterprises. It organizes its business into six reportable business segments: the Compute segment, which consists of general purpose servers for multi-workload computing and workload-optimized... Subscribe to learn more
Accelerate the vendor selection process
Get a clear picture of the competition in a market and discover which vendors are best-suited for your sourcing needs. Our supplier profiles include hard-to-find financial ranges for private companies, cover public company data and feature an interactive competitor matrix.
Procurement Management KPIs for the Security Software Market
Managing vendor performance throughout the contract period is easier when tracking specific key performance indicators (KPIs). For example, buyers should monitor Average Response Time and Customer Concentration. Buyers may experience better performance throughout their contracts if they establish service level agreements (SLAs) based on Availability and other factors.
| KPI | Level of Importance (1-5) | Measurements | Key Considerations |
|---|---|---|---|
| Average Response Time |
|
Mean time to detect Number of issues |
This measures the amount of time it takes for the software to notice or respond to security threats. Since troubleshooting issues often arise when working with new software, a faster response time is crucial to operational efficiency. |
| Customer Concentration |
|
Revenue per customer (RPC) Total revenue |
The customer concentration represents the amount of revenue associated with a single customer. The customer concentration can be used to determine the need to diversify client portfolios. It is recommended that the customer concentration remains at or below 10.0%. |
Questions to Ask During Procurement Negotiations
How can I gain leverage during negotiations?
Quality Control
How do you measure the effectiveness of your software?
How do you define a security breach? How many of these security breaches have occurred with your software?
Customer Support
Will I have access to technical support at all times?
What qualifications do your support professionals have?
Installation
Does the installation of your security suite require assistance from your company?
What is the average length of time needed for installation?
The ultimate prep for procurement negotations
View all 26 negotiation questions for this category when you subscribe.
Security Software RFP Guidelines
What should my RFP include?
Organizational Overview
Buyers should outline the details of their organization, including the number of employees, office location(s) and operating hours.
Buyers should state the reasons for purchasing new security software.
Statement Of Need
Buyers should provide a list of required features that the software includes (e.g., the ability to detect malware, bugs, and viruses, the ability to whitelist applications, the ability to conduct vulnerability assessments, and the ability to set up firewalls).
Buyers should specify the type of operating system(s) the software needs to be able to integrate with.
Project Budget
Buyers should specify their budget for the security software and related services.
Buyers can reference the Market Pricing and Total Cost of Ownership sections of this report for assistance in creating a budget.
The RFP process made easy
Find out how you can access RFP templates for 800+ procurement categories to start writing better, more consistent RFPs.
We display average pricing information, trends and market data.
Our Reports include:
- Opportunity assessment
- Market dynamics
- Recent developments
- Positive and warning trends
- Buyer power levers
- Price environment and market pricing
- Geographic wage rates
- Global market updates
- Total cost of ownership
- Cost structure benchmarks and analysis
- Supply chain and vendors
- Global supplier breakdown
- Market share concentration
- Regulation and business requirements
- Vendor management and KPIs
- Sourcing strategy guidance